
Update, October 10: FBI Director Kash Patel announced another arrest in the bureau’s investigation into ShinyHunters. Subsequent reporting identified Canadian cybersecurity executive Edward Dubrovsky as a suspect reportedly connected to the investigation. Dubrovsky faces federal extortion-related charges, but the FBI has not publicly established his alleged involvement in the FBIJobs.gov intrusion. The criminal complaint remains sealed. No additional Oracle PeopleSoft vulnerability has been confirmed in connection with the attack.
Reuters independently verified information belonging to more than 20 people contained in a sample of approximately 5,000 purported FBI employee records. The material reportedly identifies personnel associated with sensitive intelligence and counterintelligence work, including operations involving China, Russia and Iran, as well as human intelligence and electronic surveillance.
Reuters has also reviewed sensitive psychiatric and medical evaluation records allegedly obtained during the intrusion and partially authenticated some of the material. The records reportedly contain medical and psychological information associated with FBI personnel.
The FBI has acknowledged that ShinyHunters is claiming a compromise of FBIJobs.gov and an impact to FBI employee personally identifiable information. The bureau said investigators have not yet determined whether the initial breach occurred through a third-party provider supporting FBIJobs.gov or within the FBI’s own enterprise.
Separately, Google Threat Intelligence Group and Mandiant disclosed on September 25 that ShinyHunters, tracked as UNC6240, has resumed mass exploitation of Oracle PeopleSoft systems. Researchers observed the group deploying web shells on dozens of systems globally across government, healthcare, higher education, technology, transportation, agriculture and other sectors.
The newly documented campaign involves CVE-2026-35273, a critical PeopleSoft vulnerability that ShinyHunters previously exploited as a zero-day between May and June 2026. Mandiant found that the group modified its exploit to bypass web application firewall rules used by organizations that had attempted to mitigate the vulnerability without installing Oracle’s security update.
The campaign independently confirms that ShinyHunters continues to actively exploit PeopleSoft infrastructure at scale, but it does not confirm the group’s claim that a separate, previously unknown PeopleSoft zero-day was used to compromise the FBI. Neither the FBI nor Oracle has publicly confirmed the alleged new vulnerability, and no CVE has been assigned to the purported second flaw.
The FBI is investigating unauthorized activity affecting FBIJobs.gov after ShinyHunters claimed it breached bureau systems by exploiting a previously unknown remote code execution vulnerability in Oracle PeopleSoft.
The cybercrime group claims it used the alleged PeopleSoft zero-day for initial access before moving laterally into additional FBI systems, including FBI-managed AWS GovCloud infrastructure containing employee and applicant information.
ShinyHunters claims it stole between 2TB and 3TB of data covering current and former FBI personnel, job applicants and other internal records. It has also alleged access to systems associated with criminal justice, human resources and medical functions.
The FBI has not confirmed those broader claims. However, the bureau has acknowledged that it is investigating a cybercriminal group’s claimed compromise of FBIJobs.gov and alleged impact to FBI employee personally identifiable information.
The FBI said the point of compromise remains undetermined and that investigators are examining whether access originated through a third-party provider supporting FBIJobs.gov or within the FBI’s own enterprise.
The alleged new zero-day, claimed lateral movement into additional FBI infrastructure and reported theft of between 2TB and 3TB of data remain unverified.
FBI Jobs site allegedly defaced
ShinyHunters has provided evidence supporting at least some unauthorized activity involving the FBI’s recruitment infrastructure.
A screenshot shared by the group appears to show the FBI Jobs application website defaced with ShinyHunters branding and a message claiming that FBI employee and applicant information had been compromised.
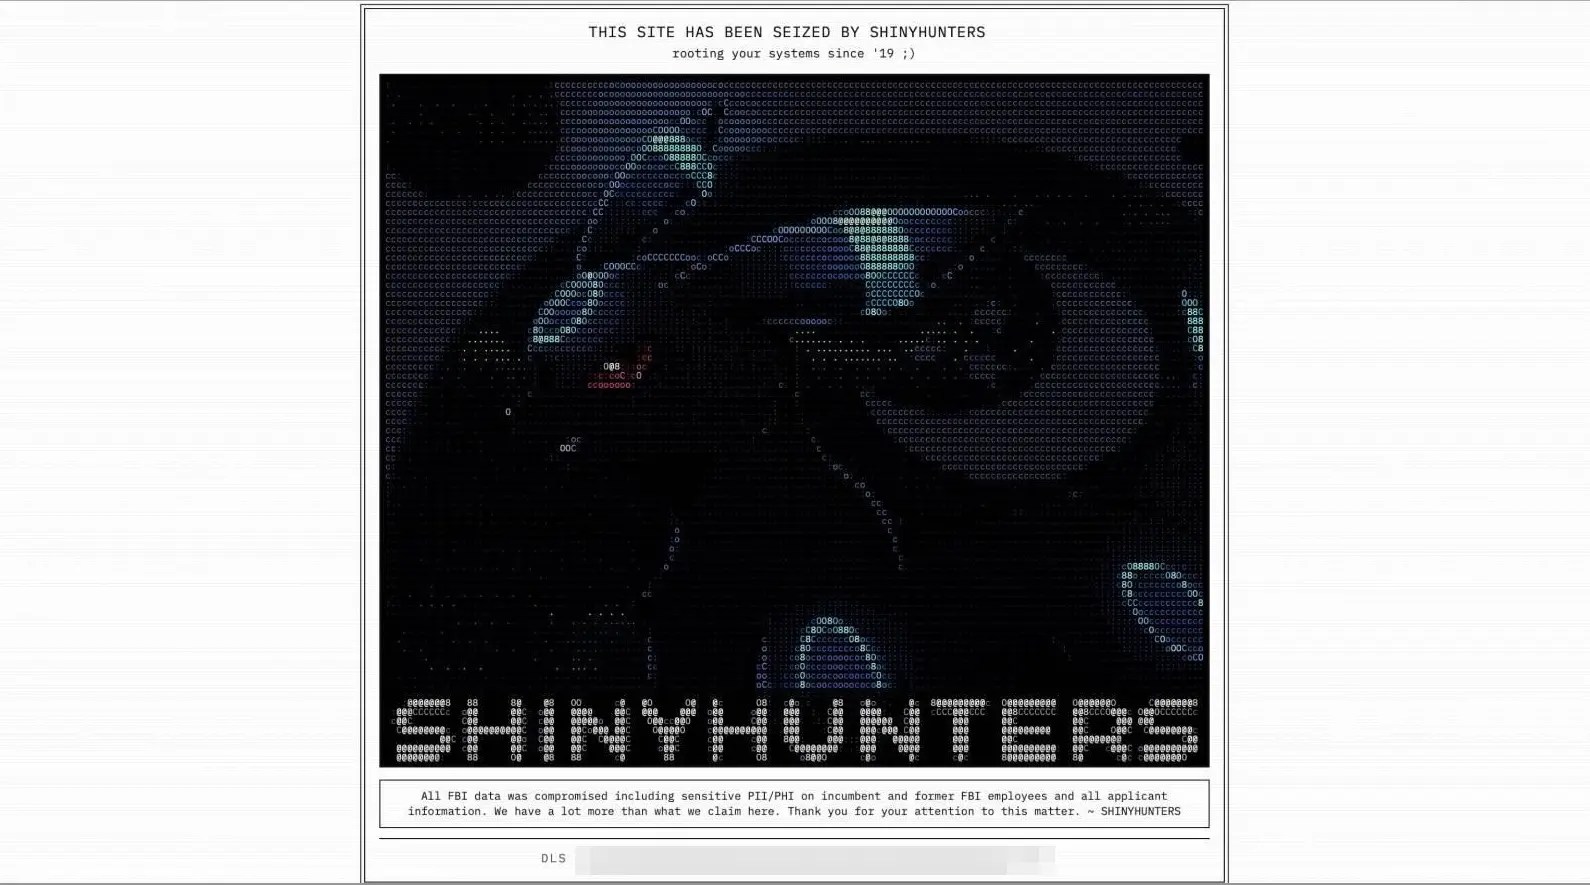
The group claims the FBI detected the intrusion and terminated access to multiple affected systems. The FBI Jobs application service was subsequently taken offline.
ShinyHunters also provided journalists with a sample containing approximately 5,000 purported FBI employee records. Subsequent reporting has provided significant corroboration that at least portions of the material contain genuine FBI personnel information.
FBI personnel data receives independent corroboration
ShinyHunters claims the stolen information includes sensitive personally identifiable information belonging to current and former FBI employees as well as individuals who applied for positions with the bureau.
Reuters independently verified information associated with more than 20 people contained in the approximately 5,000-record sample. The material reportedly includes personnel connected to sensitive intelligence and counterintelligence operations involving China, Russia and Iran, along with human intelligence and electronic surveillance-related work.
The disclosure raises concerns beyond conventional identity theft because detailed information identifying personnel involved in sensitive investigations and intelligence operations could potentially carry counterintelligence and personal security implications.
However, verification of individual records does not establish that the entire dataset is authentic or confirm ShinyHunters’ claimed method of obtaining it.
Medical and psychiatric records allegedly exposed
Additional reporting has provided evidence that the material obtained by ShinyHunters may extend beyond basic employee information.
Reuters reviewed approximately half a dozen purported FBI medical and psychiatric records supplied by ShinyHunters and was able to partially authenticate some of the information contained in the files.
The documents reportedly included a pre-employment mental health evaluation, medical and fitness-for-duty records and other sensitive health information associated with FBI personnel.
Reuters used multiple methods to corroborate portions of the material, including matching Social Security numbers against credit bureau information and confirming details involving medical professionals and employment histories.
The reporting provides additional evidence that sensitive personnel information was compromised, but the complete medical dataset has not been independently authenticated and its full scope remains unknown.
ShinyHunters claims the approximately 5,000 employee records provided to journalists represent only a small portion of a much larger collection. Its claim that the complete intrusion resulted in the theft of between 2TB and 3TB of data remains unverified.
BreachNews is not publishing personal information, employee records, medical information or other sensitive data allegedly obtained during the incident.
FBIJobs.gov uses PeopleSoft and AWS GovCloud
Public FBI documentation independently confirms that the infrastructure underlying the bureau’s recruitment system uses technologies identified in ShinyHunters’ claims.
An FBI privacy impact assessment for FBIJobs.gov and the FBI Candidate Gateway states that the system is hosted using Amazon Web Services Government Cloud and uses Oracle PeopleSoft HRS 9.2 and an Oracle database.
The Candidate Gateway is used for job applications and maintains sensitive applicant information, while the broader recruitment environment integrates with other FBI human resources systems.
The documentation confirms that PeopleSoft and AWS GovCloud are legitimate components of the FBI recruitment environment, but it does not establish that ShinyHunters exploited PeopleSoft, gained access to AWS GovCloud or moved laterally into other FBI systems as claimed.
ShinyHunters claims a new PeopleSoft zero-day
The most significant unresolved technical allegation is ShinyHunters’ claim that it discovered another previously unknown vulnerability in Oracle PeopleSoft capable of remote code execution.
The group claims it discovered the flaw shortly before the FBI intrusion and used it for initial access. ShinyHunters has also claimed that the vulnerability remained unpatched and could be used against other organizations running affected PeopleSoft environments.
ShinyHunters further claims it attempted to remove evidence of its activity from compromised servers, potentially complicating efforts to identify the vulnerability and reconstruct the initial attack path.
Neither Oracle nor the FBI has publicly confirmed that a new PeopleSoft vulnerability was responsible for the FBIJobs.gov incident.
No publicly documented CVE has been assigned to the alleged second vulnerability, and independent security researchers have not publicly reproduced or documented the purported flaw.
Google confirms renewed ShinyHunters PeopleSoft attacks
While the vulnerability allegedly used against the FBI remains unconfirmed, Google Threat Intelligence Group and Mandiant have confirmed that ShinyHunters is conducting a separate mass exploitation campaign against Oracle PeopleSoft environments.
On September 25, Google reported renewed exploitation of CVE-2026-35273 by UNC6240, its designation for ShinyHunters. The critical vulnerability was originally exploited by the group as a zero-day between May 27 and June 9 before Oracle released an out-of-band security update.
Mandiant said the latest campaign targets organizations that attempted to protect vulnerable PeopleSoft servers using web application firewall rules but did not install Oracle’s security update.
Researchers found that ShinyHunters modified requests to the vulnerable PeopleSoft Environment Management Hub endpoint by URL-encoding part of the /PSEMHUB/ path. That allowed requests to bypass some string-based firewall rules before being decoded and processed normally by the PeopleSoft application server.
The campaign has resulted in web shells being deployed on dozens of systems globally across higher education, technology, IT services, healthcare, agriculture, transportation and government organizations.
Google advised PeopleSoft administrators to install Oracle’s security update rather than relying on web application firewall rules as a substitute for patching.
The findings establish that ShinyHunters remains capable of actively exploiting PeopleSoft systems at scale. However, CVE-2026-35273 is the previously disclosed vulnerability used during the group’s earlier campaign and should not be confused with the separate zero-day ShinyHunters claims it used against the FBI.
Google’s latest findings do not establish a technical connection between CVE-2026-35273 and the FBIJobs.gov incident.
Attack framed as retaliation for FBI warning
ShinyHunters says the FBI intrusion was retaliation for FBI reporting concerning the group’s operations and extortion tactics.
The group disputes FBI descriptions involving exaggerated access claims, harassment of victims and their families, swatting and its relationship with the broader cybercriminal ecosystem commonly referred to as “The Com.”
ShinyHunters demanded that the FBI correct or remove information it described as inaccurate and gave the bureau approximately one week to comply.
The group maintains that its actions against the FBI were not financially motivated and has denied that the demand constitutes extortion.
Those statements represent ShinyHunters’ characterization of its own activity and do not override the FBI’s assessment of the group.
On September 24, ShinyHunters issued what it described as its final statement regarding the dispute, saying it was “highly confident” it had achieved its goal and that “we got what we wanted.”
However, the group also said five days remained for the FBI to comply with its request and declined to explain what it would do if the bureau did not comply. The statement therefore does not establish that the FBI met ShinyHunters’ demand.
ShinyHunters said it would no longer respond to press inquiries about the incident or provide updates concerning other datasets it claims to possess.
FBI has faced previous high-profile compromises
The latest incident follows previous compromises involving systems and communications associated with the bureau and its leadership.
Earlier this year, BreachNews reported that Iran-linked hackers allegedly breached FBI Director Kash Patel’s personal email account, highlighting the intelligence value associated with communications belonging to senior U.S. officials.
The bureau has also faced attacks targeting infrastructure used for sensitive law enforcement operations. BreachNews previously reported on the confirmed compromise of an FBI wiretap system by China-linked hackers during a broader telecommunications espionage campaign.
Those incidents provide no evidence supporting ShinyHunters’ latest allegations, but they illustrate the potential consequences if access to sensitive FBI personnel or operational infrastructure is ultimately confirmed.
Evidence of FBI data theft grows, but key technical claims remain unverified
The FBI’s acknowledgement of the investigation, independent verification of portions of the employee sample and partial authentication of purported medical records provide substantially more evidence than was available when ShinyHunters first announced the incident.
At the same time, the most consequential elements of the group’s account remain unresolved.
There is still no independent confirmation that ShinyHunters exploited a new Oracle PeopleSoft zero-day to enter FBIJobs.gov, moved laterally into FBI-managed AWS GovCloud infrastructure or obtained the full 2TB to 3TB of data it claims to possess.
Google and Mandiant’s confirmation of renewed ShinyHunters exploitation of PeopleSoft demonstrates that the group is actively compromising vulnerable PeopleSoft environments, but the confirmed campaign involves the previously disclosed CVE-2026-35273 rather than the separate vulnerability claimed in connection with the FBI.
The FBI claim emerged alongside other recent ShinyHunters extortion activity. BreachNews separately reported on the group’s claim that it stole sensitive data from Fresenius Medical Care, which the group threatened to publish following a September 25 deadline.
BreachNews will continue monitoring for additional confirmation from the FBI, Oracle or CISA, technical information concerning the alleged PeopleSoft zero-day, further evidence concerning the scope of the stolen data and any additional organizations potentially affected by the group’s PeopleSoft campaigns.


